MPLS Configuration Guide
Introduction
The Multiprotocol Label Switching (MPLS) protocol is used on Internet Protocol (IP) backbone networks. MPLS uses connection-oriented label switching on connectionless IP networks. By combining Layer 3 routing technologies and Layer 2 switching technologies, MPLS leverages the flexibility of IP routing and the simplicity of Layer 2 switching.
MPLS is based on Internet Protocol version 4 (IPv4). The core MPLS technology can be extended to multiple network protocols, such as Internet Protocol version 6 (IPv6), Internet Packet Exchange (IPX), and Connectionless Network Protocol (CLNP). "Multiprotocol" in MPLS means that multiple network protocols are supported.
MPLS is used for tunneling but not a service or an application. MPLS supports multiple protocols and services. Moreover, it ensures security of data transmission.
MPLS Configuration
Static LSP
Operation | Command | Description |
|---|---|---|
Configure IPv4 Route Forwarding with MPLS Labeling | ip route A.B.C.D/M|A.B.C.D gw label number | number: MPLS label ID to be marked, configuration range: 16 to 1048575 |
Configure IPv6 Route Forwarding with MPLS Labeling | ipv6 route X:X::X:X/M gw label number | |
Configure MPLS Static Label Processing Policy | mpls lsp number {A.B.C.D|X:X::X:X} {number|explicit-null|implicit-null} | explicit-null: The MPLS label in the neighbor notification message will be set to explicit-null (0). Upon receiving the message, the neighbor will automatically drop this MPLS label. implicit-null: Inform the neighbor that it is currently the second-to-last hop in the MPLS path and pop the MPLS label here. |
Dynamic LDP
Operation | Command | Description |
|---|---|---|
Enter MPLS LDP view | mpls ldp | |
Configure the router-id of MPLS LDP | router-id ip-address | ip-address: Name the router-id in the format of an ipv4 address |
Enter ipv4/ipv6 address-family | address-family ipv4|ipv6 | |
Configure the IPv4/IPv6 addresses advertised by the LDP address family | discovery transport-address ip-address | |
Establish a neighbor relationship with a remote LDP neighbor | neighbor ip-address targeted | |
L2VPN
Operation | Command | Description |
|---|---|---|
Configure static PW | pseudowire static name | |
Configure the local and remote labels for static pseudowires | mpls label local number remote number | number: Value range: 16–1048575 |
Enter ipv4/ipv6 address-family | address-family ipv4|ipv6 | |
Configure the static remote neighbor address for the static PW | neighbor {A.B.C.D|X:X::X:X} | |
Configure dynamic PW | pseudowire name | |
Configure the dynamic PW's pw-id | pw-id ID | The PW-ID configured on PE devices connected to adjacent ends must be consistent for the PW state to be up. |
Configure dynamic PW lsr-id | neighbor lsr-id A.B.C.D | |
Configure different L2VPN types—VPLS and VPWS—based on specific usage scenarios | L2vpn name type {vpls|vpws} | vpls: Virtual Private LAN Service (VPLS) is a point-to-multipoint Layer 2 Virtual Private Network (L2VPN). Vpws: Virtual Private Network service is a point-to-point L2VPN. |
Add PW members to the existing L2VPN | member pseudowire name | |
Add an AC interface to the existing L2VPN | member interface {ethernet|vlan|link-aggregation} | VPLS only supports VLAN interfaces, while VPWS only supports physical interfaces and LAG interfaces. |
L3VPN
Operation | Command | Description |
|---|---|---|
Enter bgp configuration view | router bgp id | |
Enter ipv4/ipv6 MPLS VPN view | address-family {ipv4|ipv6} vpn | |
Activate the MPLS VPN neighbor | neighbor {A.B.C.D|X:X::X:X} activate | |
Enter ipv4/ipv6 address-family | address-family {ipv4|ipv6} unicast | |
Configure MPLS VPN Label Assignment Method | label vpn export {auto|allocation-mode {per-vrf|per-nexthop}|Label-number} | auto: Automatically assign MPLS labels to routes. allocation-mode per-vrf: Routes are assigned labels based on the VRF; routes within the same VRF are assigned the same label. allocation-mode per-nexthop: Assign labels based on the next hop of the route; routes with the same next hop are assigned the same label. Label-number: Manually set the MPLS label assigned to the route |
Configuring RD Parameters for an MPLS VPN | rd vpn export {as-number:number|ip-address:number} | RD parameters are designed to resolve conflicts where internal networks at both ends of a VPN share the same route segment. RD is combined with the VPN prefix (VPNv4 address) to form a unique VPNv4 address. This combination of RD and VPN prefix creates a new routing entry, enabling each VPN route to be uniquely identified. |
Configuring the RT Parameters for an MPLS VPN | rt vpn {import|export|both} {A.B.C.D:MN|EF:OPQR|GHJK:MN} | import: Configure RT parameters for receiving VPN routes export: Configure RT parameters for sending VPN routes RT parameters control the identifiers used for exporting and importing VPN routes, ensuring that VPN routes are correctly sent and received between different VPNs. |
Export/Import VPN Routes | {export|import} vpn | |
Display and Maintenance
Operation | Command |
|---|---|
View MPLS label information | show mpls table |
View MPLS LDP neighbor relationships | show mpls ldp neighbor [detail] |
View MPLS LDP label information | show mpls ldp binding |
View MPLS L2VPN information | show mpls l2vpn |
View MPLS PW information | show mpls pseudowires [detail] |
View the routing and MPLS label information for all VRFs currently configured on the device | show {ipv4|ipv6} route vrf all |
Example of Reflect-acl Configuration
Network Requirements
The network topology is simple and stable, and the three router devices are MPLS backbone network devices. It is required to create a stable public network tunnel on the backbone network to carry MPLS tunnel services.
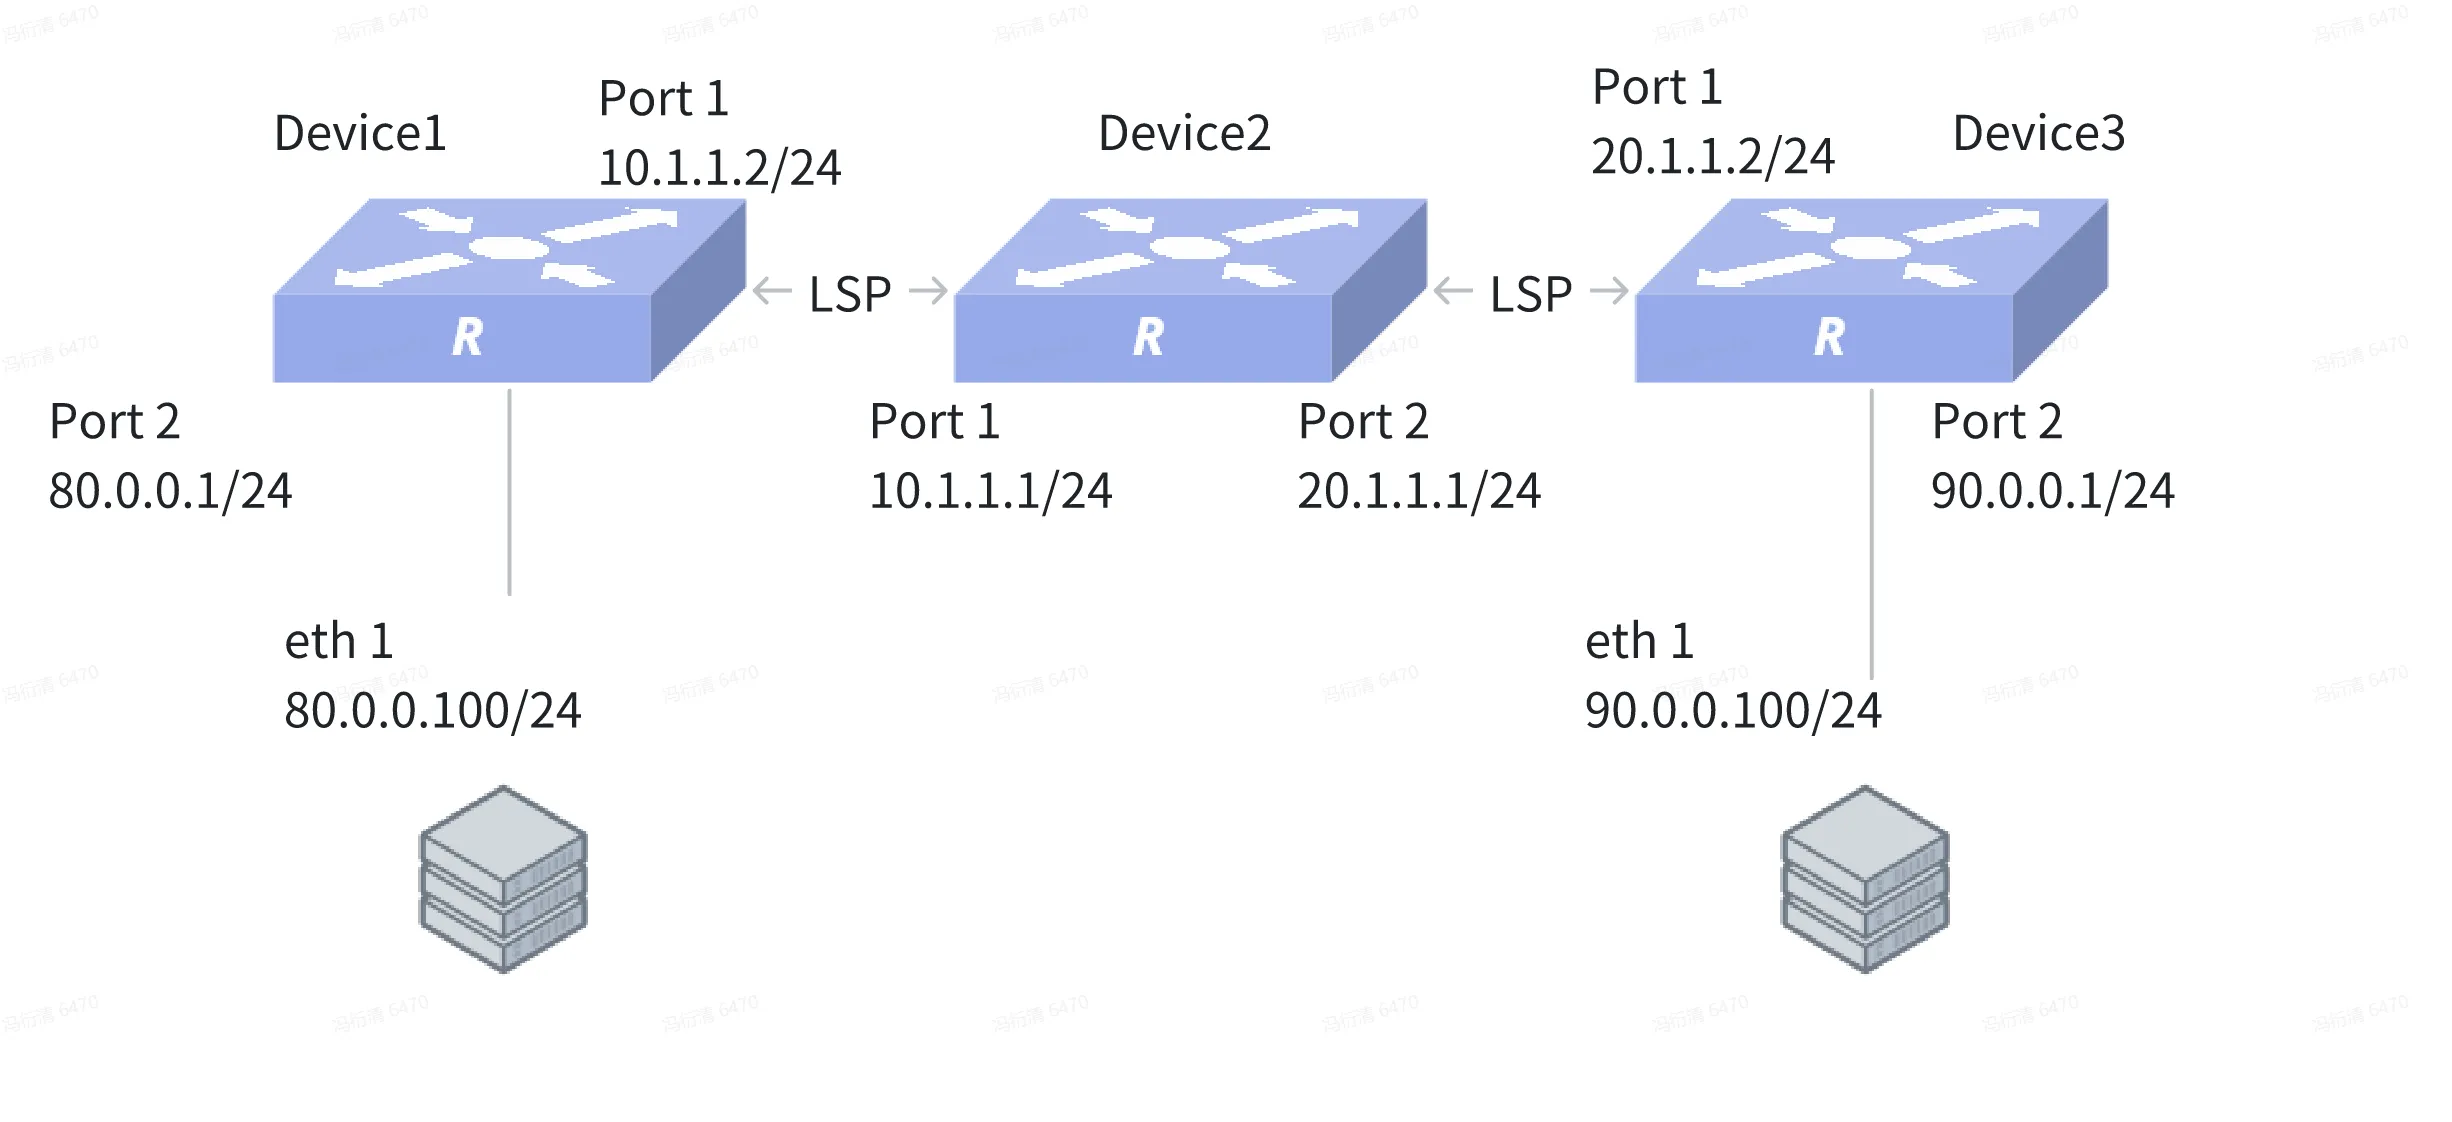
Procedure
Dveice 1
sonic(config)# interface ethernet 7
sonic(config-if-7)# ip address 80.0.0.1/24
sonic(config)# interface ethernet 15
sonic(config-if-15)# ip address 10.1.1.2/24
sonic(config-if-15)# mpls enable
sonic(config)# ip route 90.0.0.0/24 10.1.1.1 label 16
Dveice 2
sonic(config)# interface ethernet 1
sonic(config-if-1)# ip address 10.1.1.1/24
sonic(config-if-1)# mpls enable
sonic(config)# interface ethernet 3
sonic(config-if-3)#  ip address 20.1.1.1/24
sonic(config-if-3)#  mpls enable
sonic(config)# mpls lsp 16 90.0.0.100 implicit-null
sonic(config)# mpls lsp 17 80.0.0.100 implicit-null
Dveice 3
sonic(config)# interface ethernet 1
sonic(config-if-1)#  ip address 90.0.0.1/24
sonic(config)# interface ethernet 3
sonic(config-if-3)# ip address 20.1.1.2/24
sonic(config-if-3)#  mpls enable
sonic(config)# ip route 80.0.0.0/24 20.1.1.1 label 17
Example of MPLS L2VPN VPLS Configuration
Network Requirements
Device1, Device2, and Device3 are PE devices of the IP/MPLS backbone network. MPLS L2VPN services need to be deployed on Device1, Device2, and Device3 to interconnect VPN sites. Therefore, local LDP sessions need to be configured between LSRs to establish LDP LSPs to carry VPN services.
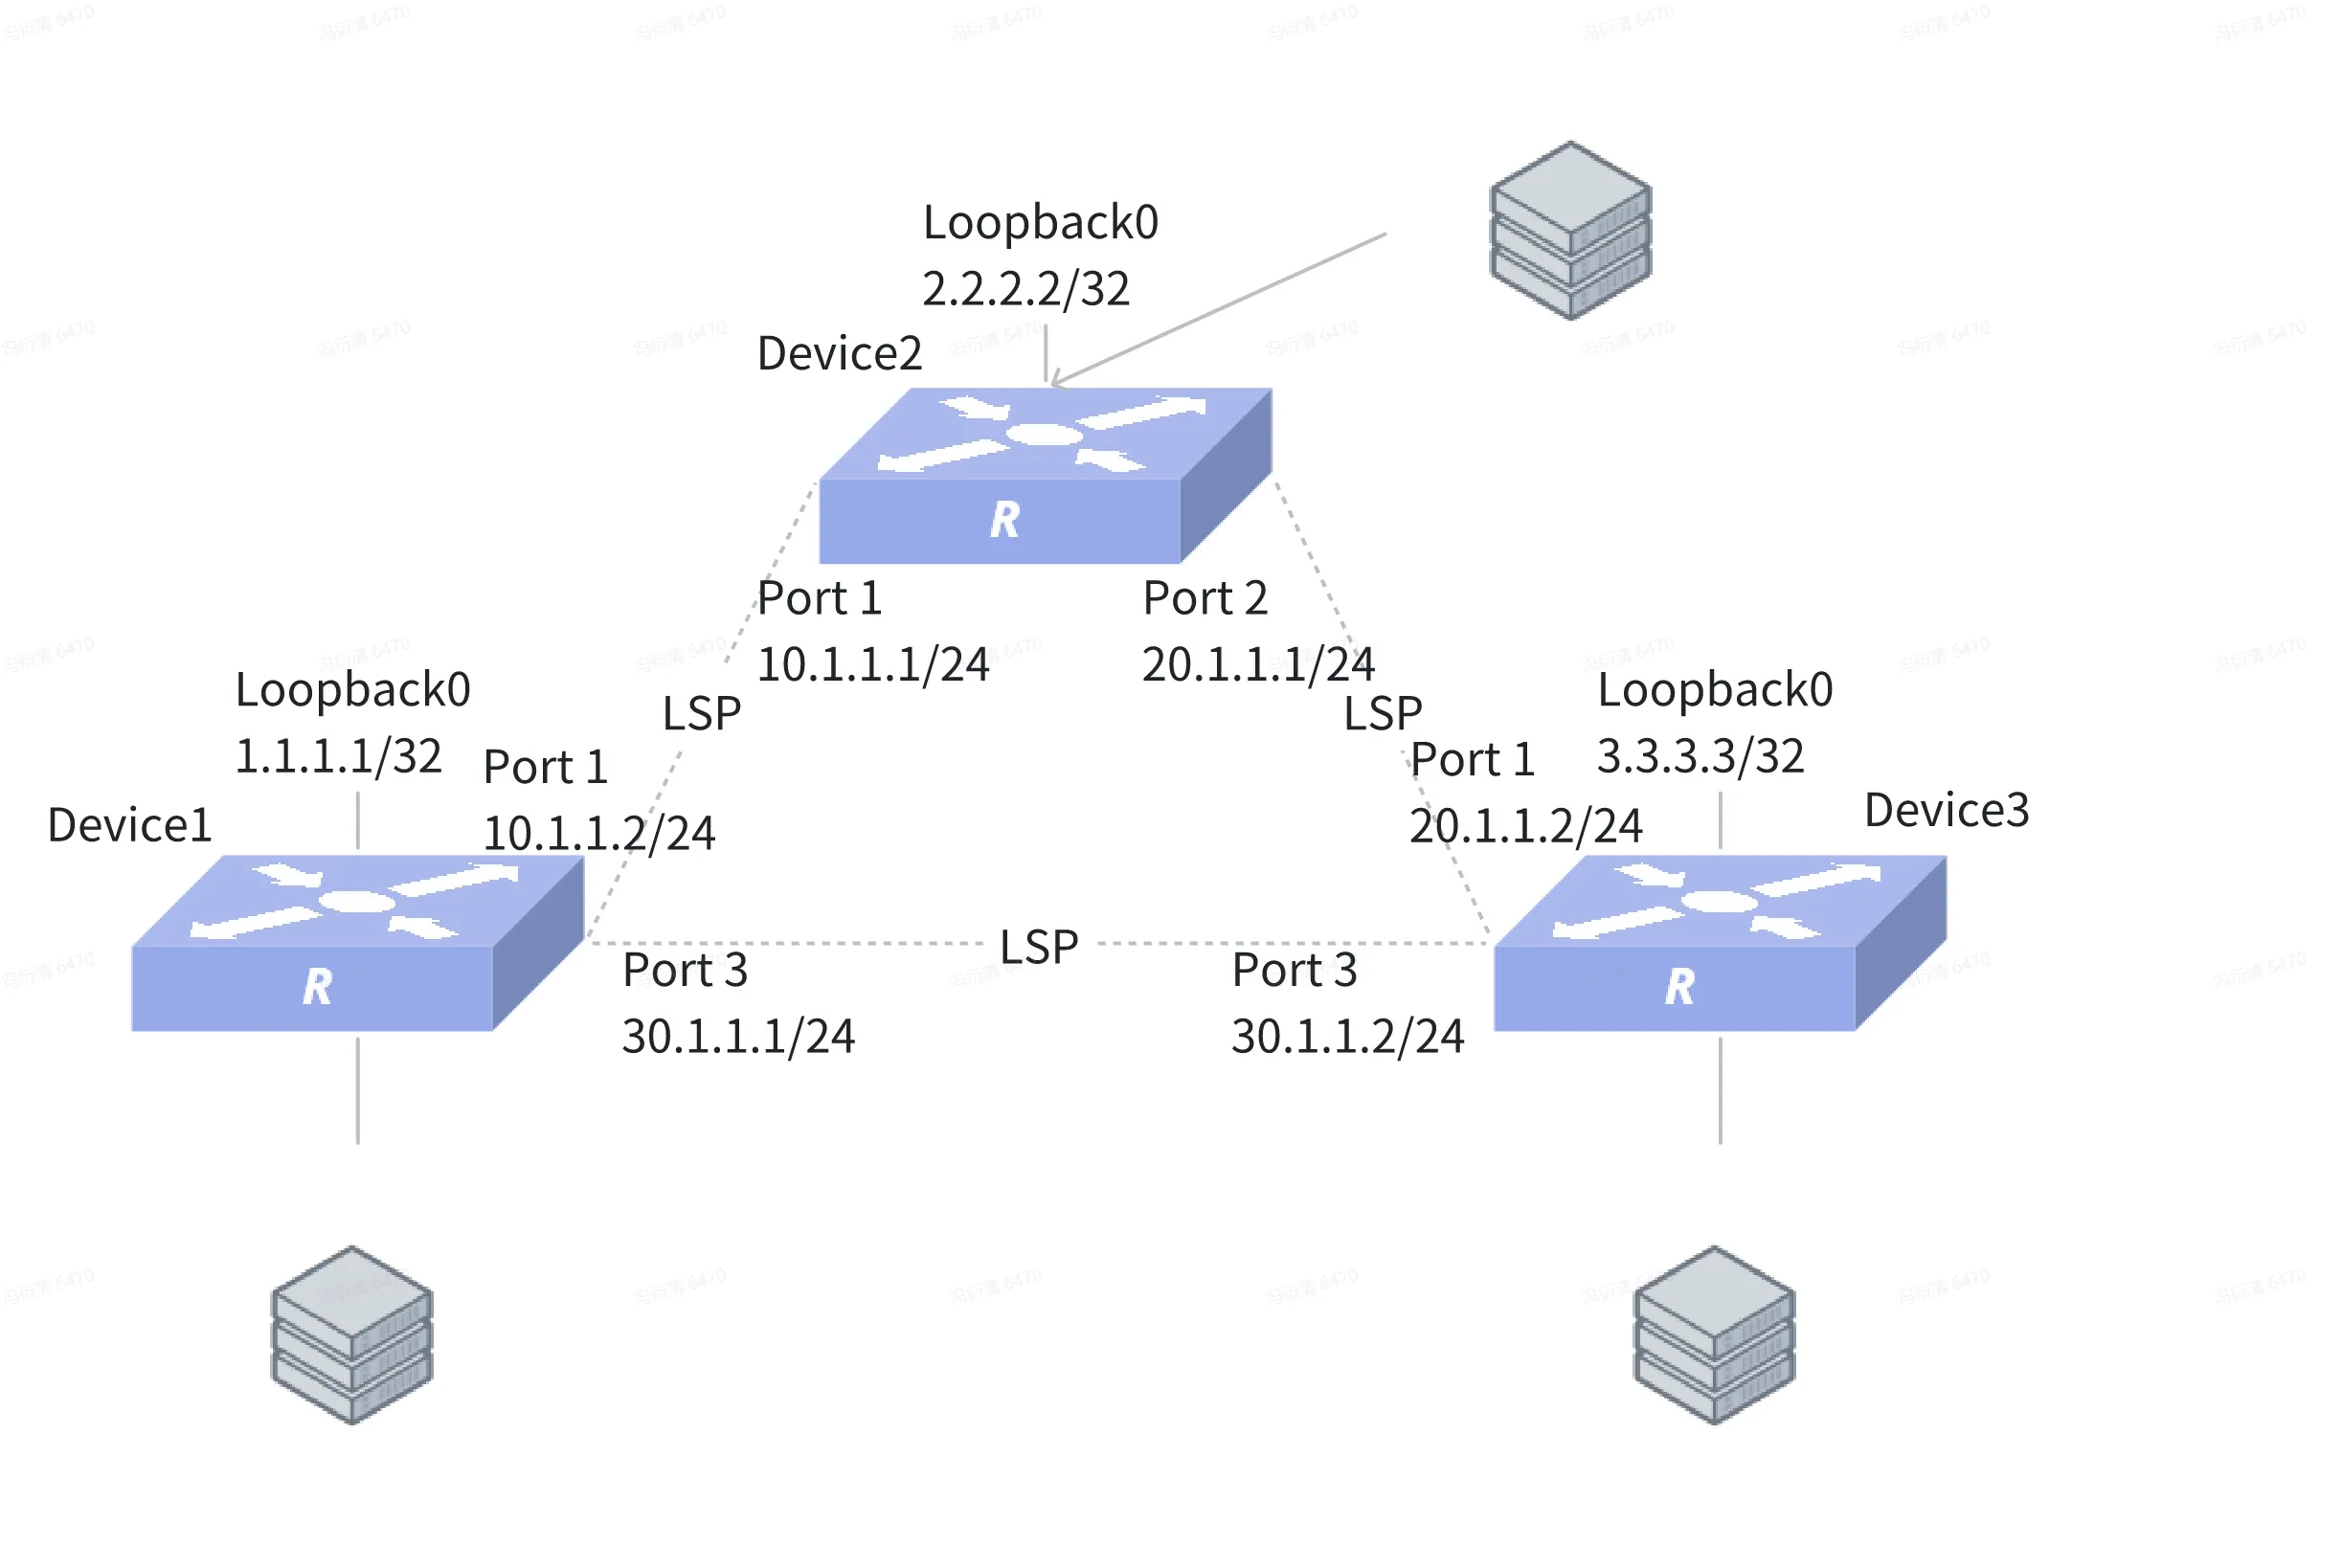
Procedure
Device 1
sonic(config)#interface ethernet 7
sonic(config-if-7)#  switchport access vlan 100
sonic(config)#interface ethernet 16
sonic(config-if-16)#  ip address 10.1.1.2/24
sonic(config-if-16)# mpls ldp
sonic(config-if-16)# ip ospf area 1
sonic(config-if-16)# mpls enable
sonic(config)#interface loopback 0
sonic(config-loif-0)# ip address 1.1.1.1/32
sonic(config)# vlan 100
sonic(config)# l2vpn test type vpls
sonic(config-l2vpn)# member interface vlan 100
sonic(config-l2vpn)# member pseudowire 219
sonic(config-l2vpn)# member pseudowire 220
sonic(config)#router ospf
sonic(config-router)# redistribute connected
sonic(config)# mpls ldp
sonic(config-ldp)# router-id 1.1.1.1
sonic(config-ldp)# address-family ipv4
sonic(config-ldp-af)# discovery transport-address 1.1.1.1
sonic(config-ldp-af)# neighbor 3.3.3.3 targeted
sonic(config-ldp-af)# neighbor 4.4.4.4 targeted
sonic(config)# pseudowire 219
sonic(config-pw)# neighbor lsr-id 3.3.3.3
sonic(config-pw)# neighbor address 3.3.3.3
sonic(config-pw)# pw-id 1
sonic(config)# pseudowire 220
sonic(config-pw)# neighbor lsr-id 4.4.4.4
sonic(config-pw)# neighbor address 4.4.4.4
sonic(config-pw)# pw-id 2
Dveice 2
sonic(config)# interface ethernet 13
sonic(config-if-13)#  switchport access vlan 100
sonic(config)# interface ethernet 16
sonic(config-if-16)#  ip address 20.1.1.2/24
sonic(config-if-16)#  mpls ldp
sonic(config-if-16)#  ip ospf area 1
sonic(config-if-16)#  mpls enable
sonic(config)# interface loopback 0
sonic(config-loif-0)# ip address 3.3.3.3/32
sonic(config)# vlan 100
sonic(config)# l2vpn test type vpls
sonic(config-l2vpn)# member interface vlan 100
sonic(config-l2vpn)# member pseudowire 217
sonic(config-l2vpn)# member pseudowire 220
sonic(config)# router ospf
sonic(config-router)# redistribute connected
sonic(config)# mpls ldp
sonic(config-ldp)# router-id 3.3.3.3
sonic(config-ldp)# address-family ipv4
sonic(config-ldp-af)# discovery transport-address 3.3.3.3
sonic(config-ldp-af)# neighbor 1.1.1.1 targeted
sonic(config-ldp-af)# neighbor 4.4.4.4 targeted
sonic(config)# pseudowire 217
sonic(config-pw)# neighbor lsr-id 1.1.1.1
sonic(config-pw)# neighbor address 1.1.1.1
sonic(config-pw)# pw-id 1
sonic(config)# pseudowire 220
sonic(config-pw)# neighbor lsr-id 4.4.4.4
sonic(config-pw)# neighbor address 4.4.4.4
sonic(config-pw)# pw-id 3
Dveice 3
sonic(config)# interface ethernet 3
sonic(config-if-13)#  switchport access vlan 100
sonic(config)# interface ethernet 16
sonic(config-if-16)#  ip address 30.1.1.2/24
sonic(config-if-16)#  mpls ldp
sonic(config-if-16)#  ip ospf area 1
sonic(config-if-16)#  mpls enable
sonic(config)# interface loopback 0
sonic(config-loif-0)# ip address 4.4.4.4/32
sonic(config)# vlan 100
sonic(config)# l2vpn test type vpls
sonic(config-l2vpn)# member interface vlan 100
sonic(config-l2vpn)# member pseudowire 217
sonic(config-l2vpn)# member pseudowire 219
sonic(config)# router ospf
sonic(config-router)# redistribute connected
sonic(config)# mpls ldp
sonic(config-ldp)# router-id 4.4.4.4
sonic(config-ldp)# address-family ipv4
sonic(config-ldp-af)# discovery transport-address 4.4.4.4
sonic(config-ldp-af)# neighbor 1.1.1.1 targeted
sonic(config-ldp-af)# neighbor 3.3.3.3 targeted
sonic(config)# pseudowire 217
sonic(config-pw)# neighbor lsr-id 1.1.1.1
sonic(config-pw)# neighbor address 1.1.1.1
sonic(config-pw)# pw-id 2
sonic(config)# pseudowire 219
sonic(config-pw)# neighbor lsr-id 3.3.3.3
sonic(config-pw)# neighbor address 3.3.3.3
sonic(config-pw)# pw-id 3
Transer Device
sonic(config)# interface ethernet 1
sonic(config-if-1)# ip address 10.1.1.1/24
sonic(config-if-1)# mpls ldp
sonic(config-if-1)# ip ospf area 1
sonic(config-if-1)# mpls enable
sonic(config)# interface ethernet 2
sonic(config-if-2)# ip address 20.1.1.1/24
sonic(config-if-2)# mpls ldp
sonic(config-if-2)# ip ospf area 1
sonic(config-if-2)# mpls enable
sonic(config)# interface ethernet 3
sonic(config-if-3)# ip address 30.1.1.1/24
sonic(config-if-3)# mpls ldp
sonic(config-if-3)# ip ospf area 1
sonic(config-if-3)# mpls enable
sonic(config)# interface loopback 0
sonic(config-loif-0)# ip address 2.2.2.2/32
sonic(config)# router ospf
sonic(config-router)# redistribute connected
sonic(config)# mpls ldp
sonic(config-ldp)# router-id 2.2.2.2
sonic(config-ldp)# address-family ipv4
sonic(config-ldp-af)# discovery transport-address 2.2.2.2
Example of MPLS L2VPN VPLS Configuration
Network Requirements
PE1, PE2, and PE3 are PE devices of the IP/MPLS backbone network. MPLS L3VPN services need to be deployed on PE1, PE2, and PE3 to interconnect VPN sites. Therefore, local LDP sessions need to be configured between LSRs to establish LDP LSPs and carry VPN services.
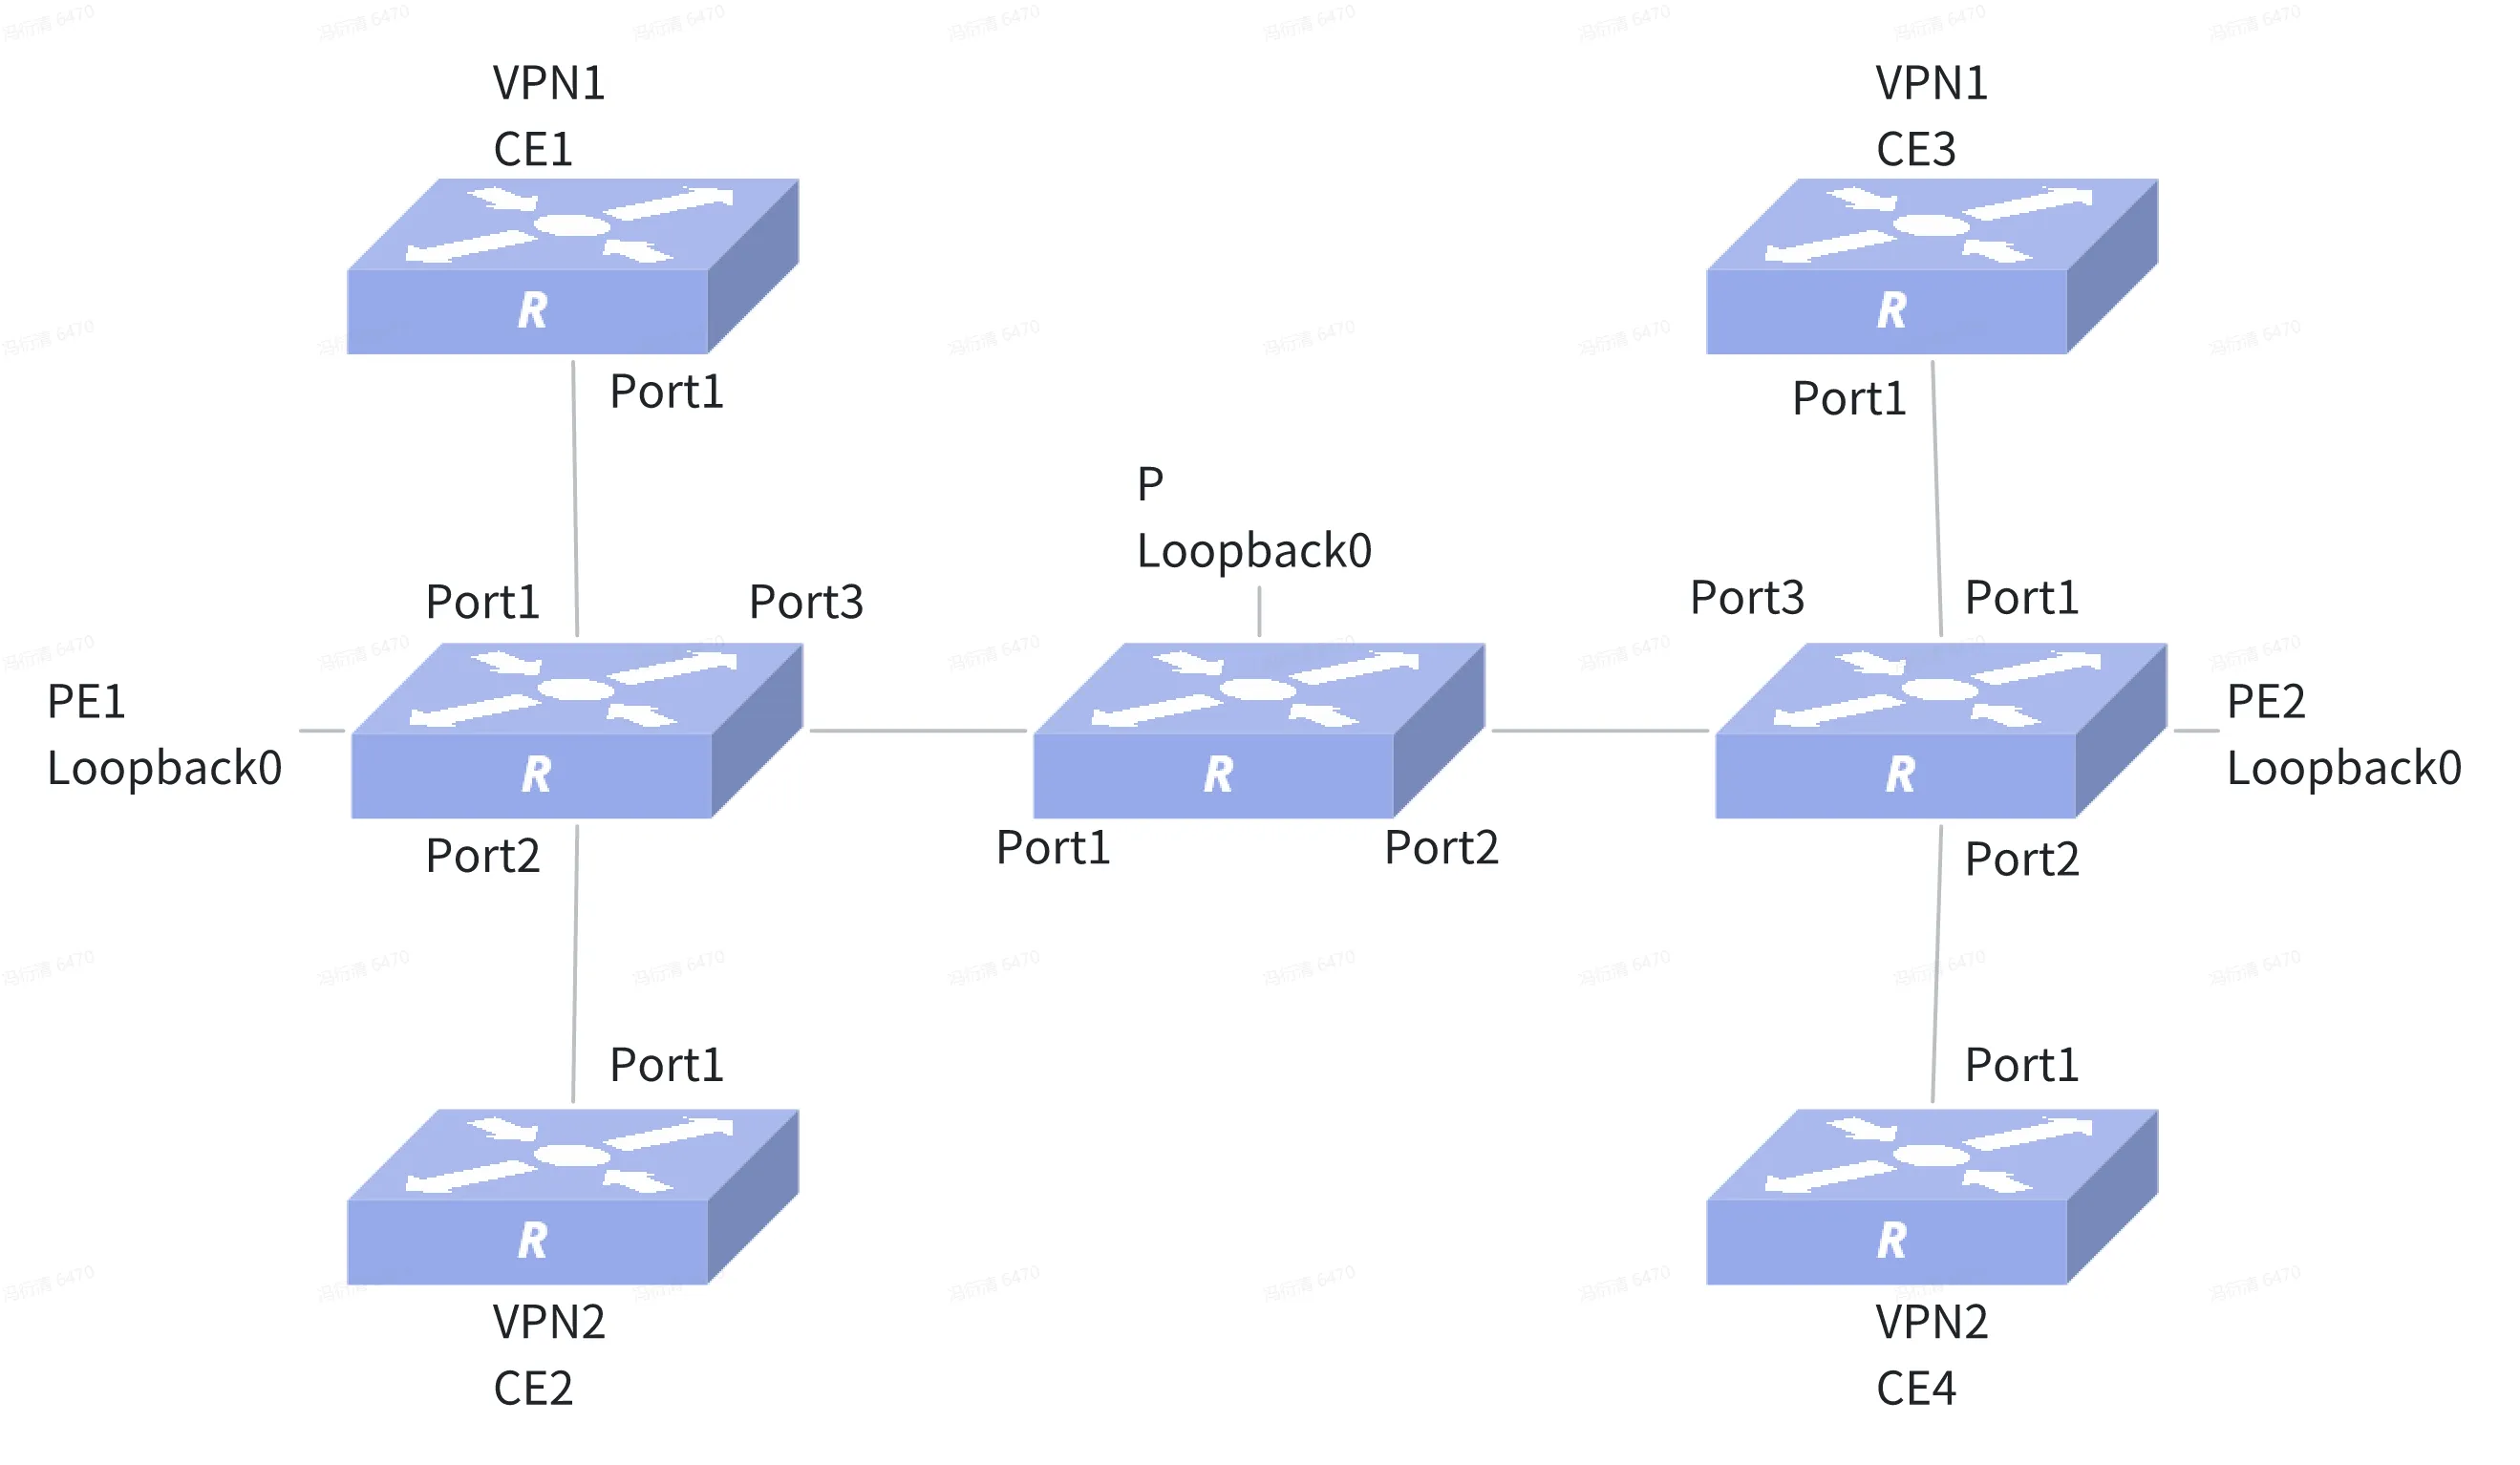
Device | Interface | IP Adderss |
|---|---|---|
CE1 | Port1 | 80.0.0.100/24 |
PE1 | Loopback0 | 1.1.1.1/32 |
Port1 | 80.0.0.1/24 | |
Port2 | 80.0.1.1/24 | |
Port3 | 10.1.1.2/24 | |
CE2 | Port1 | 80.0.1.100/24 |
P | Loopback0 | 2.2.2.2/32 |
Port1 | 10.1.1.1/24 | |
Port2 | 20.1.1.1/24 | |
CE3 | Port1 | 90.0.0.100/24 |
PE2 | Loopback0 | 3.3.3.3/32 |
Port1 | 90.0.0.1/24 | |
Port2 | 90.0.1.1/24 | |
Port3 | 20.1.1.1/24 | |
CE4 | Port1 | 90.0.1.100/24 |
Procedure
Device 1
sonic(config)# vrf l3vpn
sonic(config)# vrf l3vpn1
sonic(config)# interface ethernet 13
sonic(config-if-13)# ip address 80.0.0.1/24
sonic(config-if-13)# vrf l3vpn
sonic(config)# interface ethernet 14
sonic(config-if-14)# ip address 110.0.0.1/24
sonic(config-if-14)# vrf l3vpn1
sonic(config)# interface ethernet 16
sonic(config-if-16)# ip address 10.1.1.2/24
sonic(config-if-16)# mpls ldp
sonic(config-if-16)# ip ospf area 1
sonic(config-if-16)# mpls enable
sonic(config)# interface loopback 0
sonic(config-loif-0)# ip address 1.1.1.1/32
sonic(config)# router bgp 1
sonic(config-router)#  bgp router-id 1.1.1.1
sonic(config-router)#  no bgp ebgp-requires-policy
sonic(config-router)#  neighbor 3.3.3.3 remote-as 1
sonic(config-router)#  neighbor 3.3.3.3 update-source 1.1.1.1
sonic(config-router)#  address-family ipv4 vpn
sonic(config-router-af)#  neighbor 3.3.3.3 activate
sonic(config)# router bgp 1 vrf l3vpn
sonic(config-router)#  no bgp ebgp-requires-policy
sonic(config-router)#  neighbor 80.0.0.100 remote-as 220
sonic(config-router)#  address-family ipv4 unicast
sonic(config-router-af)#  redistribute connected
sonic(config-router-af)#  label vpn export auto
sonic(config-router-af)#  rd vpn export 1.1.1.1:1
sonic(config-router-af)#  rt vpn import 3.3.3.3:2
sonic(config-router-af)#  rt vpn export 1.1.1.1:1
sonic(config-router-af)#  export vpn
sonic(config-router-af)#  import vpn
sonic(config)# router bgp 1 vrf l3vpn1
sonic(config-router)#  no bgp ebgp-requires-policy
sonic(config-router)#  neighbor 110.0.0.100 remote-as 221
sonic(config-router)#  address-family ipv4 unicast
sonic(config-router-af)#  redistribute connectd
sonic(config-router-af)#  label vpn export auto
sonic(config-router-af)#  rd vpn export 110.0.0.1:3
sonic(config-router-af)#  rt vpn import 100.0.0.1:4
sonic(config-router-af)#  rt vpn export 110.0.0.1:3
sonic(config-router-af)#  export vpn
sonic(config-router-af)#  import vpn
sonic(config)# router ospf
sonic(config-router)# redistribute connected
sonic(config)# mpls ldp
sonic(config-ldp)# router-id 1.1.1.1
sonic(config-ldp)# address-family ipv4
sonic(config-ldp)# discovery transport-address 1.1.1.1
P
sonic(config)# interface ethernet 1
sonic(config-if-1)# ip address 10.1.1.1/24
sonic(config-if-1)# mpls ldp
sonic(config-if-1)# ip ospf area 1
sonic(config-if-1)# mpls enable
sonic(config)# interface ethernet 2
sonic(config-if-2)# ip address 20.1.1.1/24
sonic(config-if-2)# mpls ldp
sonic(config-if-2)# ip ospf area 1
sonic(config-if-2)# mpls enable
sonic(config)# interface loopback 0
sonic(config-loif-0)# ip address 2.2.2.2/32
sonic(config)#router ospf
sonic(config-router)# redistribute connected
sonic(config)# mpls ldp
sonic(config-ldp)# router-id 2.2.2.2
sonic(config-ldp)# address-family ipv4
sonic(config-ldp-af)# discovery transport-address 2.2.2.2
PE2
sonic(config)# vrf l3vpn
sonic(config)# vrf l3vpn1
sonic(config)# interface ethernet 10
sonic(config-if-10)# ip address 90.0.0.1/24
sonic(config-if-10)# vrf l3vpn
sonic(config)# interface ethernet 12
sonic(config-if-12)# ip address 100.0.0.1/24
sonic(config-if-12)# vrf l3vpn1
sonic(config)# interface ethernet 16
sonic(config-if-16)# ip address 20.1.1.2/24
sonic(config-if-16)# mpls ldp
sonic(config-if-16)# ip ospf area 1
sonic(config-if-16)# mpls enable
sonic(config)# interface loopback 0
sonic(config-loif-0)# ip address 3.3.3.3/32
sonic(config)# router bgp 1
sonic(config-router)# bgp router-id 3.3.3.3
sonic(config-router)# no bgp ebgp-requires-policy
sonic(config-router)# neighbor 1.1.1.1 remote-as 1
sonic(config-router)# neighbor 1.1.1.1 update-source 3.3.3.3
sonic(config-router)# address-family ipv4 vpn
sonic(config-router-af)# neighbor 1.1.1.1 activate
sonic(config)# router bgp 1 vrf l3vpn
sonic(config-router)# no bgp ebgp-requires-policy
sonic(config-router)# neighbor 90.0.0.100 remote-as 101
sonic(config-router)# address-family ipv4 unicast
sonic(config-router-af)# redistribute connected
sonic(config-router-af)# label vpn export auto
sonic(config-router-af)# rd vpn export 3.3.3.3:2
sonic(config-router-af)# rt vpn import 1.1.1.1:1
sonic(config-router-af)# rt vpn export 3.3.3.3:2
sonic(config-router-af)# export vpn
sonic(config-router-af)# import vpn
sonic(config)# router bgp 1 vrf l3vpn1
sonic(config-router)# no bgp ebgp-requires-policy
sonic(config-router)# neighbor 100.0.0.100 remote-as 100
sonic(config-router)# address-family ipv4 unicast
sonic(config-router-af)# redistribute connected
sonic(config-router-af)# label vpn export auto
sonic(config-router-af)# rd vpn export 100.0.0.1:4
sonic(config-router-af)# rt vpn import 110.0.0.1:3
sonic(config-router-af)# rt vpn export 100.0.0.1:4
sonic(config-router-af)# export vpn
sonic(config-router-af)# import vpn
sonic(config)# router ospf
sonic(config-router)# redistribute connected
sonic(config)# mpls ldp
sonic(config-ldp)# router-id 3.3.3.3
sonic(config-ldp)# address-family ipv4
sonic(config-ldp-af)# discovery transport-address 3.3.3.3
CE1
sonic(config)# interface ethernet 11
sonic(config-if-11)# ip address 80.0.0.100/24
sonic(config)# router bgp 220
sonic(config-router)# no bgp ebgp-requires-policy
sonic(config-router)# neighbor 80.0.0.1 remote-as 1
sonic(config-router)# address-family ipv4 unicast
sonic(config-router-af)# redistribute connected
CE2
sonic(config)# interface ethernet 13
sonic(config-if-13)# ip address 90.0.0.100/24
sonic(config)# router bgp 101
sonic(config-router)# no bgp ebgp-requires-policy
sonic(config-router)# neighbor 90.0.0.1 remote-as 1
sonic(config-router)# address-family ipv4 unicast
sonic(config-router-af)# redistribute connected
CE3
sonic(config)# interface ethernet 2
sonic(config-if-2)# ip address 110.0.0.100/24
sonic(config)# router bgp 221
sonic(config-router)# no bgp ebgp-requires-policy
sonic(config-router)# neighbor 110.0.0.1 remote-as 1
sonic(config-router)# address-family ipv4 unicast
sonic(config-router-af)# redistribute connected
CE4
sonic(config)# interface ethernet 12
sonic(config-if-12)#  ip address 100.0.0.100/24
sonic(config)# router bgp 100
sonic(config-router)# no bgp ebgp-requires-policy
sonic(config-router)# neighbor 100.0.0.1 remote-as 1
sonic(config-router)# address-family ipv4 unicast
sonic(config-router-af)# redistribute connected