Ansible Tool Configuration Guide
Preface
This document provides a detailed guide on deploying and configuring the Ansible automation tool.
Target Audience
This manual is primarily intended for the following engineers:
• Solution planners and implementers
• Network administrators responsible for network configuration and maintenance
• Test personnel
Relevant personnel should possess the following competencies:
• Familiarity with Asterfusion PacketBroker network switch products
• Understanding of relevant computer networking principles
Applicable Hardware Models
Standard Products
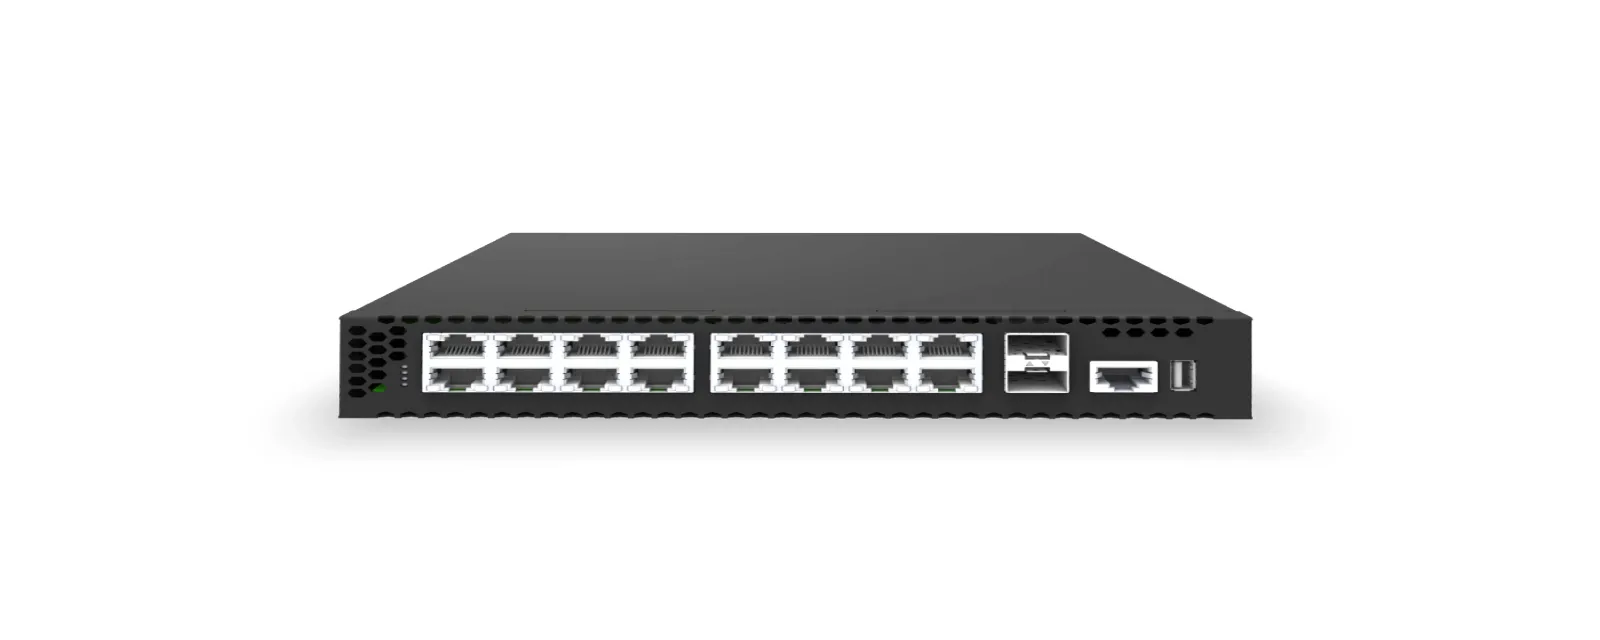
16x1G RJ45 PoE+@150W 3 Access Switch, 2x10Gb SFP+ Uplinks, Enterprise SONiC Distribution
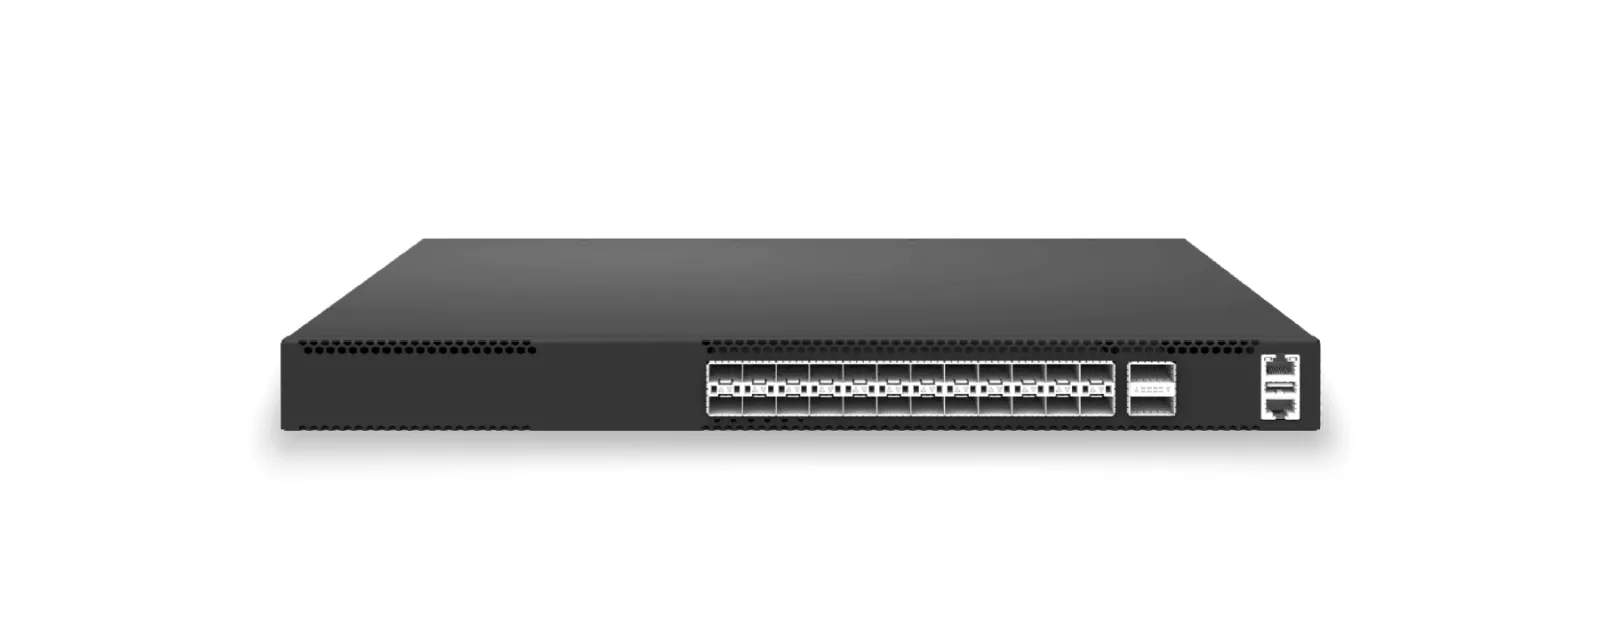
24 x 25Gb SFP28/ 10Gb SFP+, 2x 100Gb QSFP28 Uplinks, L3 Core/Leaf Switch, Marvell Aldrin3 Chip
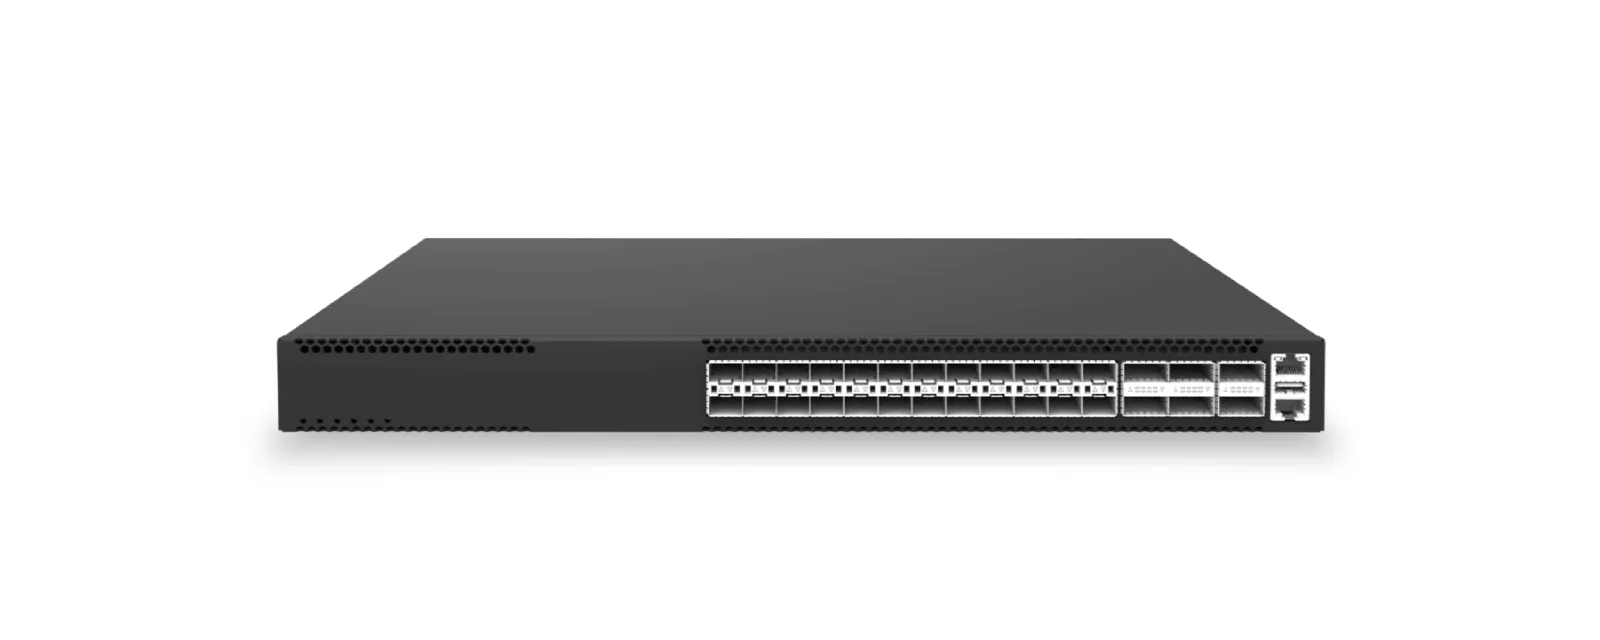
24x10G SFP+ L3 Leaf & Core switch, 6 x 100G QSFP28 /40G QSFP+ Uplinks, SONiC NOS, Marvell Prestera Aldrin2 Chip
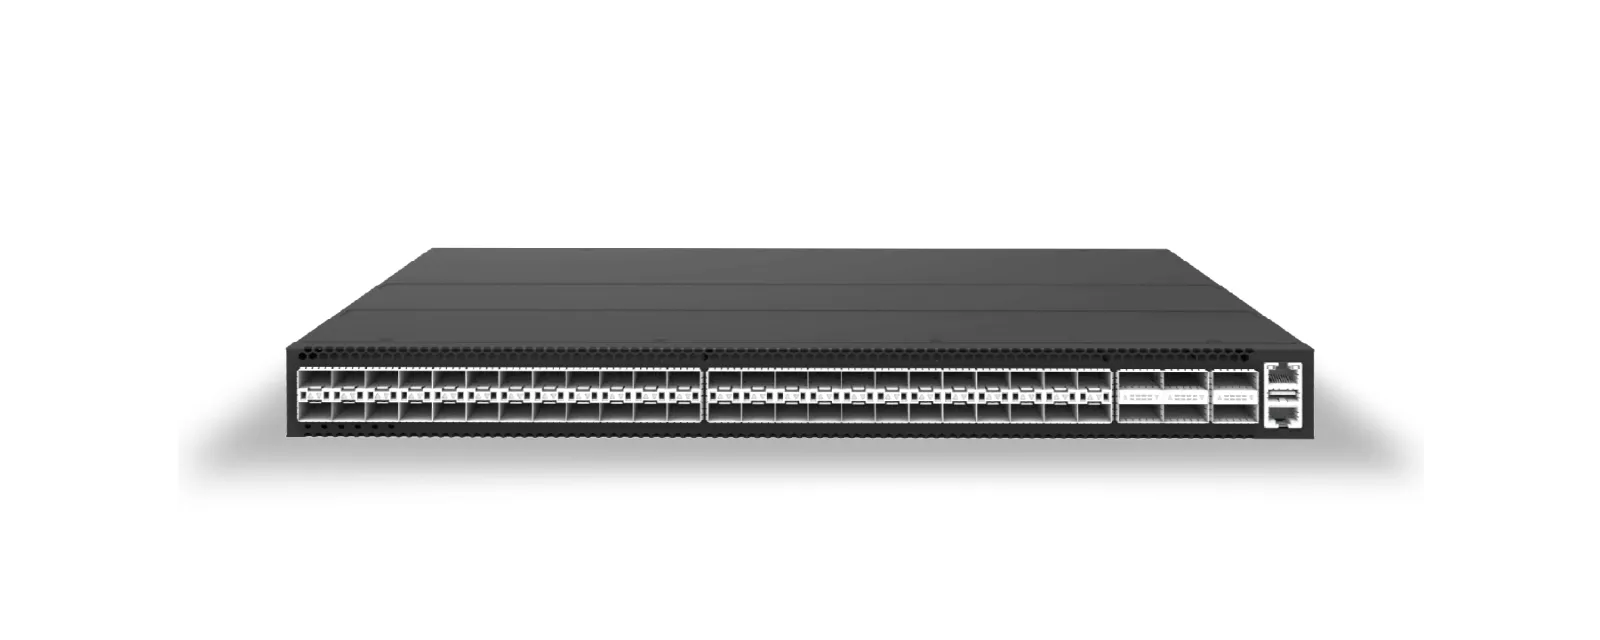
48x 10Gb SFP+, 6x 100Gb QSFP28/40Gb QSFP+ L3 Leaf Core Switch, Enterprise SONiC, Marvell Prestera Aldrin2 Chip
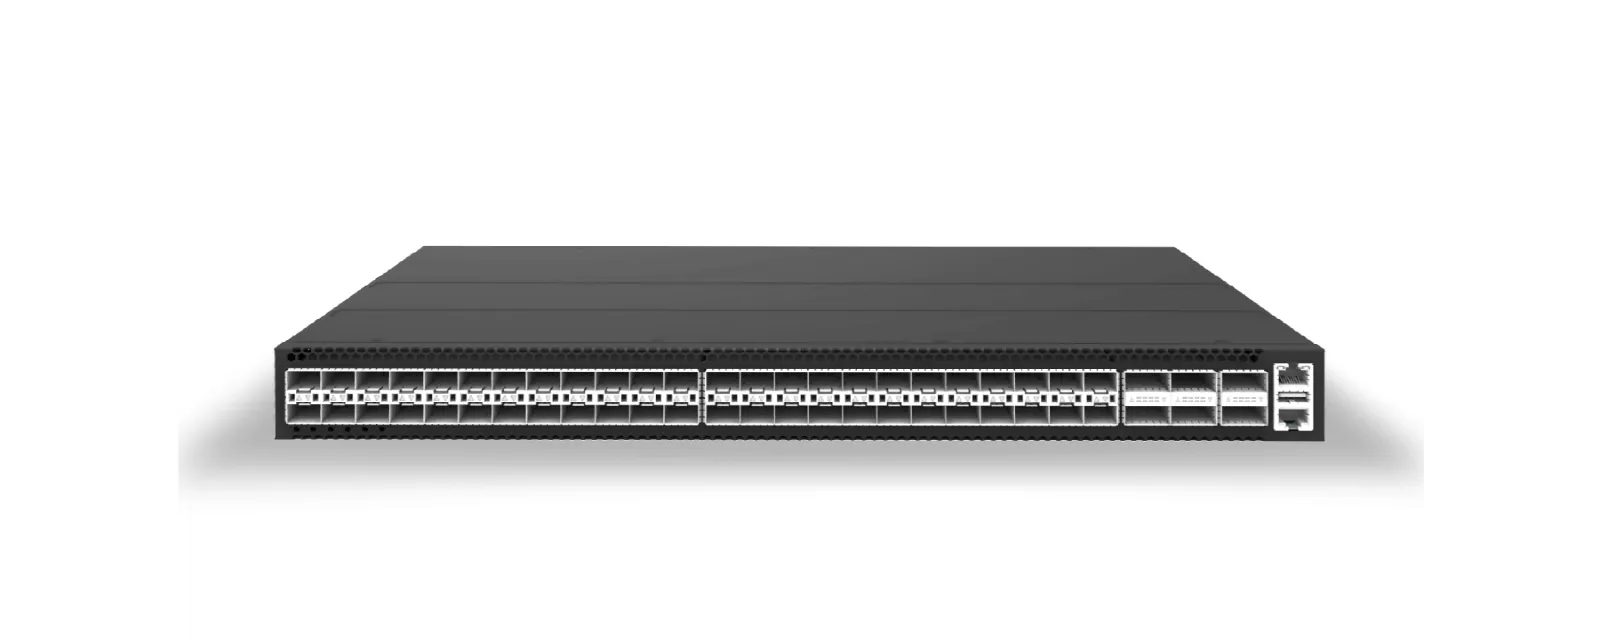
48-port 25Gb SFP28 Switch with 6x100G Uplink, Enterprise SONiC, Marvell Falcon + OCTEON 10 CN103
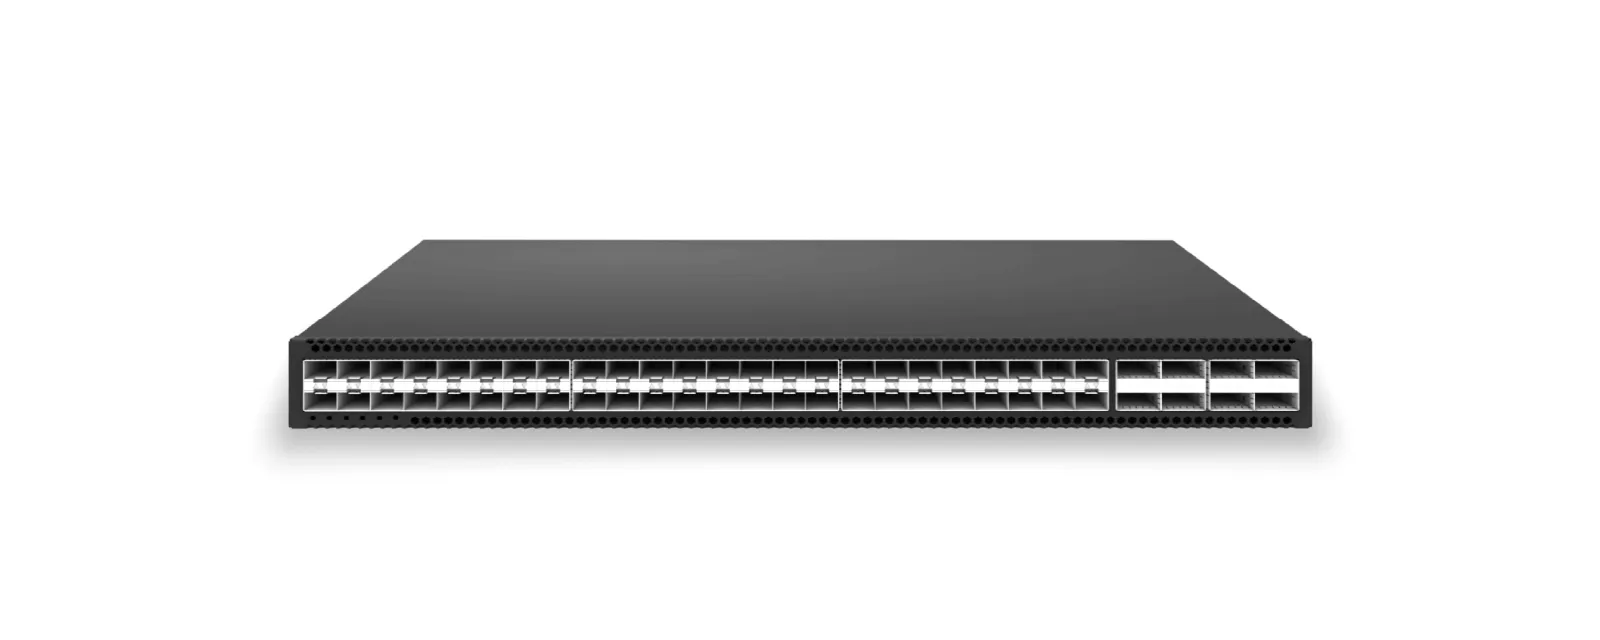
48x25Gb SFP28, 8x100Gb QSFP28 L3 Core/Spine Switch, Enterprise SONiC Ready, Marvell Falcon
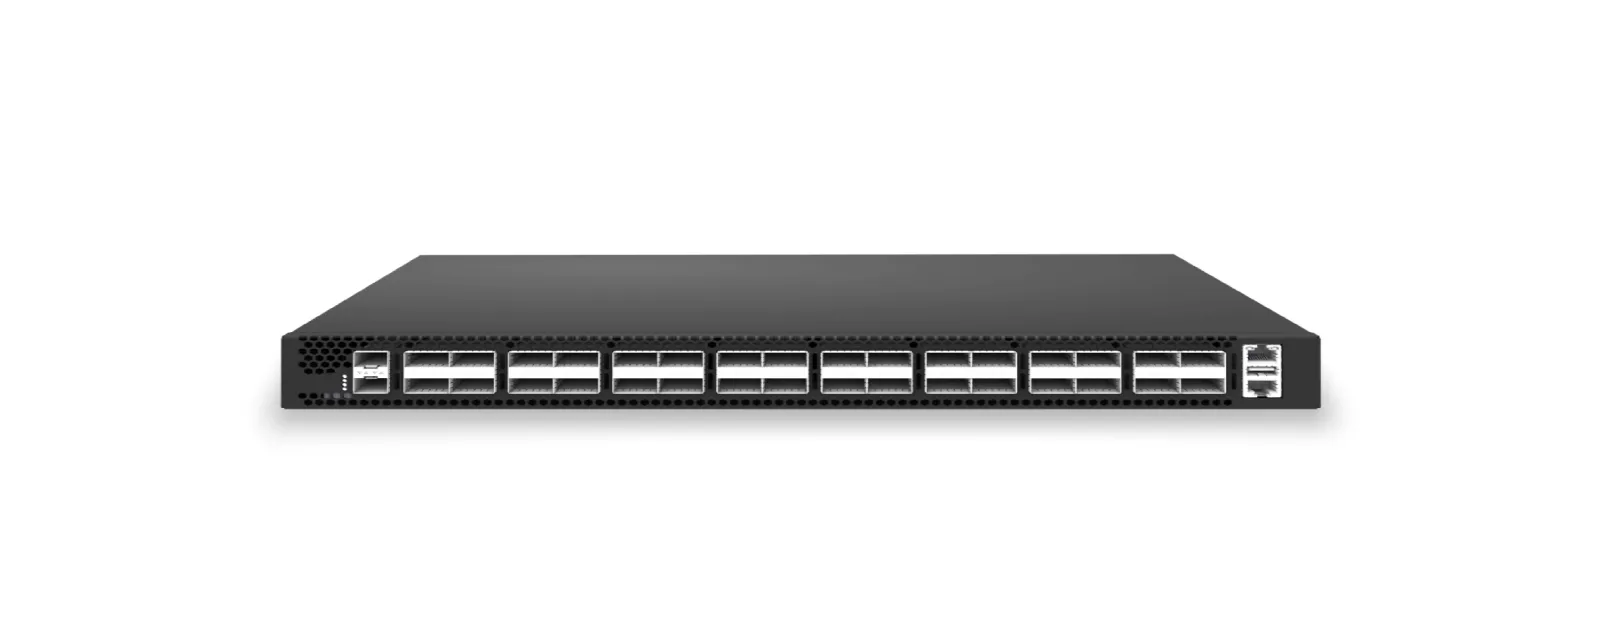
32x100Gb QSFP28 Spine and Core Switch Enterprise SONiC Ready Marvell Falcon
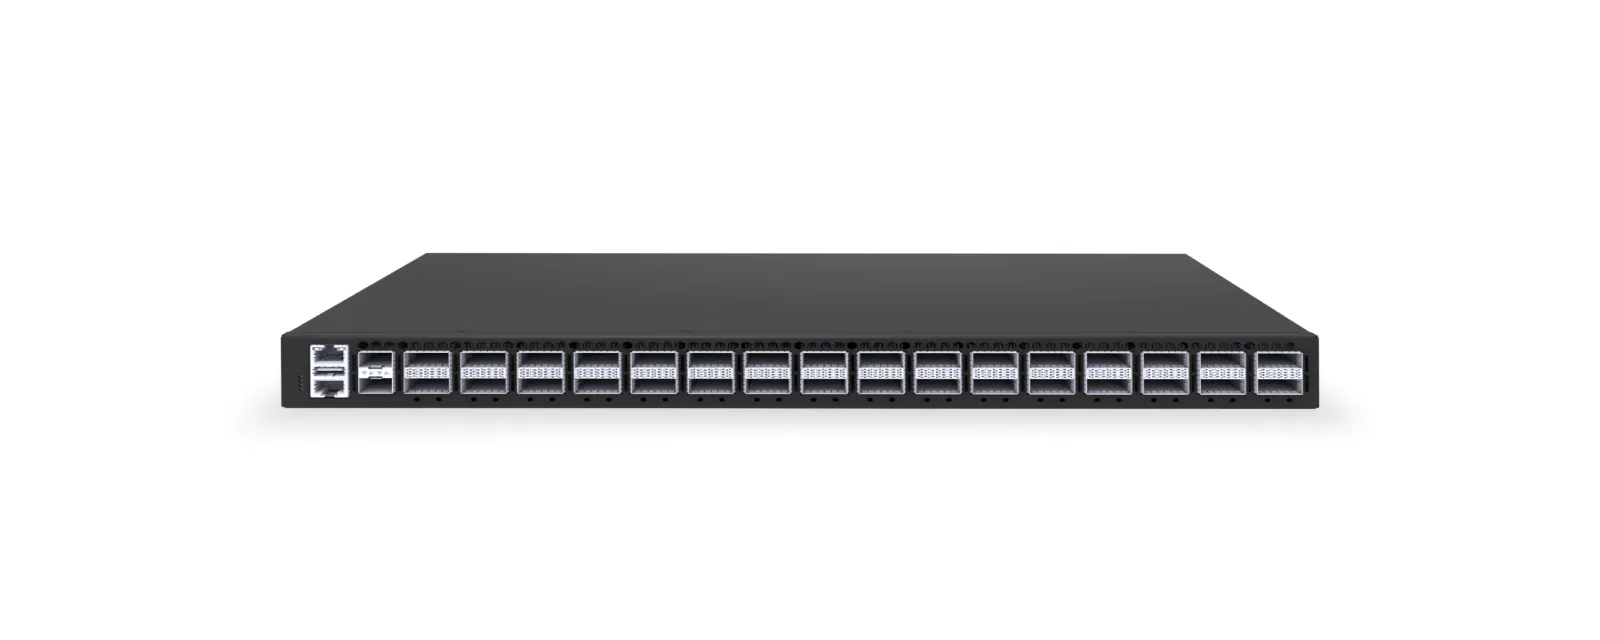
32-port 400 GbE QSFP-DD L3 Spine/Core Switch, Enterprise SONiC Ready, Marvell Falcon
Environment Deployment
Ansible is an automation tool that can configure devices by invoking sonic-cli. Configuration synchronization between the command line, controller, and WEB UI can be guaranteed when the command-line format meets the requirements.
Deploy Ansible on the server
This section uses Rocky Linux 9.6 (Blue Onyx) running on a virtual machine as an example.
- Install ansible
pip3 install ansible- The required files are as follows. You may directly edit the files or extract the attachments. The relevant file structure is as follows:
eric@mypc:\~\$ tree
.
├── ansible.cfg
├── group_vars
│   └── sonic.yml
├── host_vars
│   └── sonic1.yml
├── inventory
├── library
│   └── sonic_klish.py
└── site.yml
3. ansible.cfg Specify the device information file as inventory
[defaults]
inventory = inventory
host_key_checking = False
retry_files_enabled = False
gathering = explicit
stdout_callback = yaml- inventory Specify the IP address, username, and password of the remote device.
[sonic]
sonic1 ansible_host=192.168.1.103 ansible_user=admin ansible_password=asteros
5. group_vars/sonic.yml No changes needed.
# group_vars/sonic.yml
host: "{{ ansible_host }}"
user: "{{ ansible_user }}"
password: "{{ ansible_password }}"- In host_vars/sonic1.yml, two sets of command-line configurations to be deployed are as follows:
config_vlan_cmd: |
configure
vlan 3003
end
exit

config_acl_test_cmd: |
configure
access-list L3 test1 ingress priority 500000
rule 1 packet-action permit redirect-action ethernet 11
exit

interface ethernet 11
acl test1
end
exit- library/sonic_klish.py No changes needed; simply call the CLI command.
#!/usr/bin/env python3
import tempfile, subprocess, os
from ansible.module_utils.basic import AnsibleModule

def main():
    mod = AnsibleModule(
        argument_spec=dict(commands=dict(required=True, type='str'),
                            host=dict(required=True,  type='str'),
                            user=dict(required=True,  type='str'),
                            password=dict(required=True, type='str', no_log=True)),
        supports_check_mode=False
    )
    cmds = mod.params['commands']

    host   = mod.params.get('host')
    user   = mod.params.get('user')
    passwd = mod.params.get('password')

    tmpfile = tempfile.mktemp()
    with open(tmpfile, 'w') as f:
        f.write(cmds)

    ssh_opts = "-o StrictHostKeyChecking=no -o UserKnownHostsFile=/dev/null"
    try:
        cp = ["sshpass", "-p", passwd, "scp"] + ssh_opts.split() + [tmpfile, "{}@{}:/tmp/klish.cmds".format(user, host)]
        subprocess.check_call(cp, stdout=subprocess.DEVNULL)
        exe = ["sshpass", "-p", passwd, "ssh"] + ssh_opts.split() + \
              ["{}@{}".format(user, host), "sonic-cli", "<", "/tmp/klish.cmds"]
        out = subprocess.check_output(exe, stderr=subprocess.STDOUT)
    except subprocess.CalledProcessError as e:
        mod.fail_json(msg=e.output)

    finally:
        os.unlink(tmpfile)
    mod.exit_json(changed=True, stdout=out)

if __name__ == '__main__':
    main()
- Set up the test case by adding two new tasks that call config_acl_test_cmd and config_vlan_cmd respectively.
- hosts: sonic
  gather_facts: no
  tasks:
    - name: Push klish commands
      sonic_klish:
        commands: "{{ config_acl_test_cmd }}"
        host:     "{{ host }}"
        user:     "{{ user }}"
        password: "{{ password }}"
      delegate_to: localhost
      register: result

    - name: Push klish commands 1
      sonic_klish:
        commands: "{{ config_vlan_cmd }}"
        host:     "{{ host }}"
        user:     "{{ user }}"
        password: "{{ password }}"
      delegate_to: localhost
      register: result

    - debug: var=result.stdout
- Use Case Execution
[root@localhost ansible]# ansible-playbook -v site.yml
Using /home/ryan/ansible/ansible.cfg as config file

PLAY [sonic] ******************************************************************************************************************************************************************************************************

TASK [Push klish commands] ****************************************************************************************************************************************************************************************
changed: [sonic1 -> localhost] => changed=true
  stdout: |-
    Warning: Permanently added '192.168.1.102' (RSA) to the list of known hosts.
    ...Entering cli view, please wait...
    stty: 'standard input': Inappropriate ioctl for device
    stty: 'standard input': Inappropriate ioctl for device
    sonic# configure
    sonic(config)# access-list L3 test1 ingress priority 500000
    sonic(config-L3-acl-test1)# rule 1 packet-action permit redirect-action ethernet 13
    sonic(config-L3-acl-test1)# exit
    sonic(config)# interface ethernet 13
    sonic(config-if-13)# acl test1
    sonic(config-if-13)# end
    sonic# exit
  stdout_lines: <omitted>

TASK [debug] ******************************************************************************************************************************************************************************************************
ok: [sonic1] =>
  result.stdout: |-
    Warning: Permanently added '192.168.1.102' (RSA) to the list of known hosts.
    ...Entering cli view, please wait...
    stty: 'standard input': Inappropriate ioctl for device
    stty: 'standard input': Inappropriate ioctl for device
    sonic# configure
    sonic(config)# access-list L3 test1 ingress priority 500000
    sonic(config-L3-acl-test1)# rule 1 packet-action permit redirect-action ethernet 13
    sonic(config-L3-acl-test1)# exit
    sonic(config)# interface ethernet 13
    sonic(config-if-13)# acl test1
    sonic(config-if-13)# end
    sonic# exit

TASK [Push klish commands] ****************************************************************************************************************************************************************************************
changed: [sonic1 -> localhost] => changed=true
  stdout: |-
    Warning: Permanently added '192.168.1.102' (RSA) to the list of known hosts.
    ...Entering cli view, please wait...
    stty: 'standard input': Inappropriate ioctl for device
    stty: 'standard input': Inappropriate ioctl for device
    sonic# configure
    sonic(config)# vlan 3003
    sonic(config-vlan-3003)# end
    sonic# exit
  stdout_lines: <omitted>

TASK [debug] ******************************************************************************************************************************************************************************************************
ok: [sonic1] =>
  result.stdout: |-
    Warning: Permanently added '192.168.1.102' (RSA) to the list of known hosts.
    ...Entering cli view, please wait...
    stty: 'standard input': Inappropriate ioctl for device
    stty: 'standard input': Inappropriate ioctl for device
    sonic# configure
    sonic(config)# vlan 3003
    sonic(config-vlan-3003)# end
    sonic# exit

PLAY RECAP ********************************************************************************************************************************************************************************************************
sonic1                     : ok=4    changed=2    unreachable=0    failed=0    skipped=0    rescued=0    ignored=0